Applications
Applications lists the applications in the selected environment, their addresses and whether each is serving. Select one to open its own page. The short version of adding one is Add an app or static site; the detail is below.
Add an application
Choose Add application on Applications. Every kind goes through the same four steps:
- What you are adding: WordPress, Moodle, a secret manager, or My own code.
- Its code: a connected GitHub repository and branch (its default branch is chosen for you), or a ZIP file you upload. Hosting reads it as soon as you choose it. A WordPress, Moodle or secret manager install has no code to choose; Hosting installs and sets it up for you.
- What we found: what Hosting will do, in plain sentences. It recognises a static site, a built
front-end app (React, Vue, Svelte, Astro), a Node.js app, a Python app, a PHP site and a Laravel
app. It reads the Node or PHP version your code asks for, the install your lockfile pins, the
settings your
.env.examplenames, and whether your code needs a database. The name is suggested from the repository or ZIP name, with the naming rule beside it. Each line has a Change link for the technical detail behind it, such as the start command or the port, so you only open the ones you want to change. If the folder has its ownhosting.yaml, it says so, and you can import that instead. - Review what will run, where it will answer and what it reserves from your environment's shared pool, then choose Add and deploy followed by its name (Add, for an install with no code). The written configuration and the allocation figures behind the review are under The configuration and allocation details.
The page then shows each step as it happens: connecting the code, building, starting the release and publishing the address. It says the application is live only once its address answers. Hosting keeps the configuration it wrote for you; nothing is added to your code.
An application's tabs
Selecting an application opens its page. Each tab has its own address, so a reload, a bookmark or Back returns to the same one:
| Tab | What it is for |
|---|---|
| Overview | Whether it is serving, and the next step if it is not |
| Deploy | Its code source, builds and releases — see Deploy a change. Only an application built from your code has it |
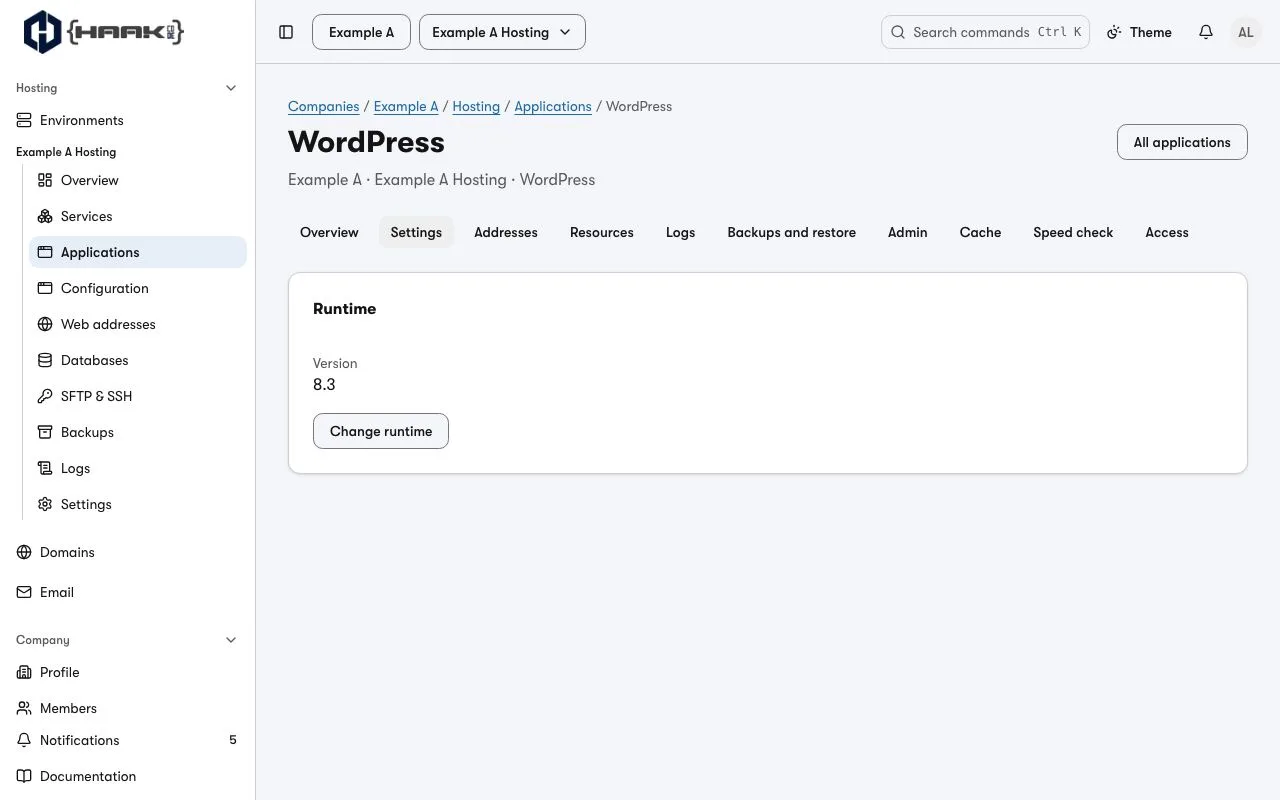
| Settings | Its environment variables, secrets, database and runtime — see Settings |
| Addresses | Its generated address and the names you own — see Web addresses |
| Resources | What it uses from the environment's pool — see Change resources |
| Logs | Its own output — see Read logs |
| Backups and restore | Its restore points and the restores it can take — see Restore a backup |
| Admin | The administrator login of an application Hosting installs, such as WordPress or Moodle |
| Cache | What the page cache stores — see Cache your site |
| Speed check | An on-demand response-time check — see Speed check |
| Access | Who has to sign in to see the site — see Site users |
| Processes | Its background workers, schedules and release tasks — see Processes |
Settings
Settings shows what the application runs with, each with its own Change button:
- Environment variables — the settings it reads at runtime.
- Declared secrets — the secret values it needs, set without being shown back.
- Database — whether it uses a database. Use a database gives it one on the environment's database server and delivers the connection settings; nothing else has to be written.
- Runtime — its Version, Start command and Port. "Detected from your code" and "Set for you" mean Hosting chose the value from your code.
The first three appear only for an application built from your code. If the application came from
its own hosting.yaml, the tab says so: change the file and resync it rather than editing here.
Speed check
Speed check measures how fast the application answers, only when you ask. Choose
Run speed check: Hosting makes three anonymous HEAD requests to the application's generated
address and reports the Median HEAD response time, what it found (caching, compression, cookies,
TLS) and, under Response samples, each request's status, timing and headers.
It checks response headers and TLS from inside the platform. It does not render pages in a browser, download page bodies or assets, follow redirects, or measure public DNS or what a visitor far away experiences. Opening the tab sends nothing to your site. Each result is a snapshot, not a trend.
Processes
Processes lists an application's Background processes: its workers, the scheduled tasks it declares and the task that runs before each release. Recent runs shows each run's Process, Status (Running, Succeeded, Failed or Timed out), when it was Scheduled, Started and Finished, its Duration, and the Reason a failed run stopped. A run stopped for running past its deadline shows as Timed out, apart from one that failed. Choose View output to read what a run printed; it is read from the platform when you ask, not stored.
Schedules lists each declared schedule, when it last ran and last succeeded. A Company Admin can Pause or Resume a schedule, or choose Run now for one extra run. A schedule never starts while its previous run is still going, and scheduled starts are approximate: a run can start late, and only recent runs are kept.
Workers, schedules and release tasks are declared in the application's configuration — see background workers, schedules and release tasks. Only an application built from your code has this tab.
Open a site
Each application has its own address. The address shown on the application is the one it will answer on:
- a generated address is created for every application and always keeps working, even while you are setting up a domain of your own. It is the address that actually serves until a name of yours is published, so it is never taken away while a name is being prepared;
- a domain name you own can be attached to one application. Choosing it records the address the application is configured with right away; the name then answers visitors once Hosting has observed its DNS pointing here and its HTTPS certificate is ready.
The application page reports those as separate facts — the chosen address, whether its DNS is ready, whether it is active, and any pending reason — rather than one "ready" state. See Web addresses for the full journey.
Sign in to WordPress or Moodle as an administrator
Every application has one administrator credential that Hosting creates and can reset.
- Open Applications, select the application and choose its Admin tab.
- It shows the sign-in address and the username.
- Choose Show password, or choose Set a new password to replace it.
Set a new password changes the credential the environment uses; the application picks it up at the next apply, and the message tells you so. Until that apply finishes, the existing password keeps working — nothing is locked out in between. If somebody changed the password inside the application itself, resetting is the reliable way back in, because a password you changed there is not the password Hosting holds.
The administrator login can install plugins and themes, change content, and read everything the application stores. Share it deliberately.
Repair stored links after importing a WordPress site
Choosing an address never rewrites your content — it records and shows the address the application is configured with and leaves the database alone. If a WordPress site was imported and still holds old hostnames inside its content (including links stored in serialized Elementor data), use the explicit Repair stored URLs action rather than editing the database by hand.
- Open the application and choose Repair stored URLs beside its selected address.
- Enter the old address to replace. You do not type the destination: Hosting reads it from the application's own selected address, so the repair follows the address you configured.
- Hosting runs a read-only check and shows the bounded result — the tables and columns it covers, how many references it found, and what it leaves alone (post GUIDs, the historical redirect log and other sites). Nothing changes during the check.
- Only a successful check lets you confirm. Confirming holds the application's writers and captures a matched recovery point before any change.
- Hosting replaces the references and then verifies that no supported reference remains. A partial or failed write keeps the hold, so a half-changed site is never served; you can retry or recover the captured state from the same progress panel, and cancel while it is still safe to do so.
- An open, unconfirmed check must be cancelled before you start another, and switching the application or company clears the draft.
The panel reports the counts and durations it actually observed, never a claim that the work is finished before it is.
Import a WordPress site of your own
A Company Admin can move an existing WordPress site onto Hosting by uploading it, rather than rebuilding it. Open the application and choose Import a WordPress site on its Backups and restore tab.
You provide two things:
- the site's database dump (
.sql); - its files, as either a single
.zipor a directory selection.
Fetch it from the old host instead
Rather than downloading the site and uploading it again, choose Or fetch it from the old host in the
same dialog (or hostingctl application import-fetch). Pick a file connection to the old host that has
passed its check, and the folder the site lives in, or give an https:// address of a .zip, .jpa,
.tar.gz or .tgz archive on a public address. Pick the site's MySQL database connection as well
(direct, through SSH, or the one found from the site); only an Akeeba .jpa carries its own database.
Hosting copies both in the background into the same private staging an upload uses, and from there the
review and confirmation below are exactly the same. Nothing is written to the old host.
Refresh from the old host (hostingctl application import-refresh) fetches the same folder and
database again into a new review. That review says what it replaces — the copy staged or imported
earlier, with its date and size — so you can bring the site up to date just before you switch DNS.
Nothing is written by the upload. Hosting stages the files privately, reads what the site is, and shows what it detected — the WordPress version, the table prefix it will adopt, and the site address recorded in its data — together with the exact consequence of confirming: this application's files and database are replaced with the uploaded site's. Uploads are bounded (3 GiB in total, up to 200,000 files) and are refused with the limit that applied rather than truncated. An untrusted upload is never executed to read its version, and it does not run with the platform's own database privileges.
Review the detected facts, then confirm. Hosting holds the application's writers, captures a recovery point, and only then replaces the files and loads the database. Progress, retry and cancel are the same controls the reviewed reset and restore use, and cancelling before a write starts leaves the application untouched. When it reports that the import itself finished:
- your own Hosting administrator and database credentials and salt keys are kept, because only the site's content is imported;
- the email settings the site stores are not changed: moving mail, MX records or a registrar to Hosting is a separate, explicit step you take yourself;
- content still holding the old address needs the Repair stored URLs action above, because Hosting does not guess how your content should be rewritten;
- a site that arrives without a root
.htaccess— typical of a site moved from an nginx host — is given WordPress's own rewrite rules, so its pages resolve here rather than answering "not found"; a site that brings its own.htaccesskeeps it; - the old host keeps serving whatever still points at it, so finish your DNS cutover when you are ready. If the old site keeps taking writes until then, stop writes there and use Refresh from the old host just before the switch, since the import replaces the database rather than merging into it.
A staged upload that you do not confirm is discarded — by Choose different files or Cancel, and otherwise by expiry. Reloading the page while a staged upload exists offers that same upload back rather than starting again.
Importing a site is not the same as restoring a backup made here: a backup restore returns this application to an earlier point of its own history. The upload is also a Hosting-side operation, so if a site still needs a shell on the old server, do that part yourself before you upload. The import does not establish that the site will run here: it reads the site's version, table prefix and recorded address, and it copies and filters the files it was given, but it does not decide the PHP extensions or plugins a site needs. Check the imported site on its own address after the import, and treat anything the site then reports as its own requirement.
Cache your site
An application's Cache view can have the platform store a repeat response instead of asking the application for it again, so a busy site answers faster. A new application starts with the cache on, using the pattern below that matches what it is: WordPress pages and assets, Moodle's theme and scripts, a static build's assets, or your own response headers for any other application. You can change its rules, set how long a stored response may be reused, or turn it off in the same view. Clearing the cache cannot remove a copy a visitor's browser already holds.
Where a cached application is WordPress, its cache is also cleared for you:
- publishing a post or page, editing one that is already published, unpublishing it, or deleting a published one clears the cache, so a visitor is not served the old page;
- installing or updating a plugin, theme or WordPress core, or switching the active theme, clears it, because those can change how a page is rendered;
- saving a draft, an autosave or a revision does not clear it: none of those is what a visitor is served;
- Clear site cache stays available while caching is on, for anything still showing an older version.
Automatic clearing is active only while HTTP caching is on for this application. With caching off, the site is not served from the cache, so there is nothing for it to clear.
Start from a template
The Cache view also offers four starting patterns for the rules that decide what is stored. Choose one, adjust its paths before you apply it, and finish exactly as you would with a rule you type yourself. Choosing a pattern changes only the rules in your unsaved draft.
- WordPress pages and assets. Rules for
/wp-includes,/wp-content/themesand/wp-content/plugins, then one rule that stores pages for visitors who are not signed in. Our WordPress images serve static files in those three directories with a public freshness of one hour by default, so those files are stored. An endpoint under the same directories is still executed and keeps its own headers, and a restrictive header the cache receives still prevents storage. Your visitors' browsers may also keep those files for up to that hour, which clearing the site cache cannot undo. A page is stored only when the request carries no cookie, has no query string and is not under sign-in, the admin area, the REST API, cart, checkout or account paths, and only when WordPress's response sets no cookie. Publishing, editing, deleting, updating and switching theme clear the stored pages automatically. Uploads are not cached, because they can hold your own members' files. - Moodle theme and scripts. Rules for Moodle's theme styles, images, fonts and JavaScript
handlers (
/theme/styles.php,/theme/image.php,/theme/font.php,/theme/yui_combo.php,/lib/javascript.phpand/lib/requirejs.php). They return the same files to every visitor and change address when the theme changes, so they are stored even for signed-in learners. Pages, sign-in and course files are not cached, because Moodle marks them private to each visitor. - Static build assets. A rule that declares
/assetspublic to every visitor, including requests that carry cookies. Change the path to your own build directory if yours is different. The HTML entry point is not cached, because the pattern ends with a rule that bypasses every other path. - Follow response headers. One rule across the whole site, which stores an eligible response only when your application declares it public.
Only the WordPress pattern stores pages, and only for visitors who are not signed in. Caching still needs the enable step and Apply, as it does with rules you type. If your draft already has rules, using a template asks before it replaces them, and Cancel keeps your saved settings.
A pattern is nothing more than those ordered rules, so a scripted client submits the same settings
it would type: hostingctl application cache-set takes the same paths, actions and windows, and the
command reference lists its flags.
The same four patterns are also a one-call shorthand on the cache endpoint: send enabled: true
with a template of wordpress, moodle, static_build or application_headers instead of a rule
list, and the platform stores that pattern's ordinary rules, which you can then edit like any rule
you typed.
Send either a template or your own rules, never both — a request carrying both is refused rather
than silently choosing one — and an unknown template name is refused with the names it does know.
An environment with several applications can be turned on in one step from the Applications view
(or PUT …/hosting/environments/{uuid}/cache with enabled and an optional template). That action
keeps any rules an application already declares and only gives a pattern to the ones that declare
nothing: the template you name, or without one the pattern that matches each application's type. It
reports what happened per application, and if one of them refuses, nothing is written at
all. It cannot turn the cache off: switching off is the per-application reset, and a bulk switch must
not delete rules it did not create.
Clear the cache from your own application
This applies to an application whose code you build or upload: publishing content, a deploy or a webhook can call the cache directly instead of waiting for the stored copy to expire, whichever language your code is written in. A WordPress application needs nothing here: its cache is cleared automatically through its cache integration, described above. A managed Moodle application has no application code of yours to call this from, so its cache relies on short freshness and expiry instead.
The platform delivers these environment variables while caching is on:
| Variable | What it is |
|---|---|
HOSTING_CACHE_PURGE_URL | The clear endpoint, already scoped to this application. It is only reachable from inside your application, not from the internet |
HOSTING_CACHE_PURGE_TOKEN | A credential that authenticates only this application. It cannot clear another application's paths, another environment's cache or anything else |
HOSTING_CACHE_PURGE_CREDENTIAL_FILE | A read-only JSON file with the current purge_url and token, scoped to this application. Read it for each clear so rotation takes effect without restarting your process |
In the environment's Cache view, Rotate purge tokens replaces the clear credentials for all
applications while they keep serving. The CLI equivalent is
hostingctl environment purge-tokens <environment-uuid> rotate --company <company> --confirm;
status reports progress. Before rotating, make custom integrations read the credential file for
each clear. A token copied at startup stops authorizing clears when its replacement applies.
Send one BAN request with the current token as a Bearer credential. The token environment
variable is a startup snapshot; long-lived applications read the file instead. WordPress does this
automatically. In Node:
import { readFile } from "node:fs/promises";

const { purge_url, token } = JSON.parse(
  await readFile(process.env.HOSTING_CACHE_PURGE_CREDENTIAL_FILE, "utf8"),
);
const response = await fetch(purge_url, {
  method: "BAN",
  headers: { Authorization: `Bearer ${token}` },
});

if (!response.ok) throw new Error(`Cache clear failed: ${response.status}`);
What the answers mean:
200— the stored copies for this application are clearing;403— the token is missing or is not this application's. An empty or unset token is refused too;503— the clear did not apply. Sending it again is safe.
You do not need to build the URL or read the Secret yourself: both variables appear in your application's environment once caching is on, and disappear when caching is turned off. Clearing is not instant for a request already in flight — that fetch can still store its response afterwards, so short freshness or a second clear is the answer, not a longer wait. A visitor's browser copy is separate and is not cleared by this.
What will be stored
The cache never decides that your application is per-user. Whether a path is stored is decided in two places that are not the same: turning the cache on needs a rule, and a running cache still stores a response on a path no rule matches when that response explicitly declares itself public.
Turning it on requires a rule for the paths you want stored — a Cache as a public asset or
Respect the origin policy rule. Turning it on with nothing declared is refused with "Nothing on
this application is declared cacheable — add a rule for the paths you want stored.", because a
cache with no declaration only looks like it works. The rule set is not the whole story at run
time: a path no rule matches is still stored when the response itself declares Cache-Control: public with a max-age or s-maxage, and a path inside an Always bypass the cache rule is
never stored. A response carrying Set-Cookie, or declaring private, no-store or no-cache,
is never stored, and a request carrying Authorization is always passed to your application. A
response is also not stored when it carries no Content-Length, or when it is larger than the
cache's per-file size limit. The Cache view states that limit for this application, so take the
current figure from there rather than assuming one.
Which applications you can have
Hosting offers managed sites and services, plus applications built from your own source. Availability depends on your environment and package; Configuration reports the runtimes that environment can apply.
For Laravel, Ruby, managed Supabase components and a secret manager, see Deploy other application types. It also shows the WordPress and Moodle creation forms.
Every kind is added through Add an application. The whole resulting allocation is checked against the environment's purchase, so an application that would overspend it is refused rather than accepted and fixed later.
A Ruby, Go or other runtime the four steps do not list is declared in the environment's configuration instead: Configure a source-built application, under the kinds in step 1, opens it. A managed WordPress or Moodle site can be created or adopted there too — see Configuration. Adopting one by its application UUID keeps its files, database identity and native administrator and database credentials; it reinstalls nothing. Removing an application always goes through Remove below, never by leaving it out of the configuration document: leaving a member out only stops configuring it, and deletes nothing.
What your code must do
Detection reads your code, but it cannot change how your server behaves. Before you add it:
| Setting | What your application must do |
|---|---|
| Install | Install from a committed lockfile, so dependency versions are pinned. |
| Start command | Start a long-running production HTTP server, not a development watcher. |
| Port | Listen on the port Hosting gives it in PORT, on 0.0.0.0 rather than only localhost. |
| Database | Read the connection settings Hosting delivers, and run its own migrations. A database connection does not create tables. |
| Files | Write uploads to declared storage. Files inside a release are replaced by the next one. |
| Secrets | Keep tokens and keys out of the repository and the ZIP; set them on the application's Settings tab. |
If the app builds browser JavaScript, settings it needs at build time are public build settings and are baked into the build; changing a runtime setting does not rewrite JavaScript already built.
Give Hosting your code
Its code, step 2 of adding an application, takes a GitHub repository connected under Company → Code sources, or a ZIP file you upload. An application's Deploy tab can later build from any of three sources:
A GitHub repository. Connect GitHub once under Company → Code sources → GitHub repositories with Connect GitHub, and choose the account and repositories the Hosting app may read. Connecting deploys nothing; a repository is used only when an application is added from it.
Upload a ZIP. Hosting reads the archive once, refuses anything unsafe or unreadable, and shows
what it measured before anything is built: the folder the project was found in, the file count and
size, and anything a build would need that is missing. Uploading builds nothing and changes nothing
that is live — an archive you never build from expires on its own. ZIP the folder that holds your
project, without build output or node_modules, and choose Build and deploy this archive when the
review looks right. To ship a change, upload the new archive and build again.
Git over SSH. This works with any Git server you can reach over SSH — GitHub, GitLab, Bitbucket
or your own. Paste the repository address (git@host:owner/repo.git or
ssh://git@host:port/owner/repo.git), the branch or tag, and a label. Hosting generates a dedicated
deploy key and shows its public half and fingerprint; add that public key to the repository as a
read-only deploy key. Nothing is fetched until you:
- Confirm the server's fingerprint. Compare the fingerprint Hosting found with the one your Git server reports, and confirm only when they match. Hosting refuses to fetch from a server whose key changed.
- Verify access (recommended). Hosting performs a real fetch with your key, so you know the key works before spending a build on it.
A push does not deploy by itself for an upload or an SSH source; build when you want the new commit. If you replace the key, install the new public key before the next build. Revoking a source stops new builds and drops a built-but-not-deployed release, and never interrupts a release that is serving.
Each source gives Hosting your code, not your data or your secrets.
Remove an application
A Company Admin removes one application with Remove beside it on Applications. The review lists what will stop answering, the directories involved, the database identity, the applications that stay, and what deliberately survives, and confirming approves that inventory's digest. The rest of the environment keeps serving. Removing an application is not the same as cancelling hosting, which ends the whole environment.
Run a PHP application you wrote
A Generic PHP application is your own PHP code served by a web server the platform owns. You declare the source, where the web tree starts, how an unmatched path is answered, and any Composer install; the platform declares the process. There is no run command, no start command and no port to set.
What the document may and may not say
A PHP application accepts source, build, env, storage, documentRoot, routing, resources
and its runtimeVersion. It refuses run, workers, cron and release by name: the platform
starts Apache or php-fpm itself, so a block nothing would execute is refused rather than stored.
Apache, php-fpm behind nginx, or FrankenPHP
Three serving shapes are offered, and the choice belongs to the application, not the environment:
| Shape | What runs | Choose it when |
|---|---|---|
Apache 2 with mod_php | One container; Apache serves the files and runs PHP in-process | Your site is written the ordinary way and you have no reason to prefer another shape |
| php-fpm behind nginx (default for YAML) | Two containers in one Pod; nginx listens on 8080 and php-fpm answers on the Pod's own loopback only | You want static files served by nginx and PHP kept out of the web server process |
| FrankenPHP (Caddy with PHP embedded) | One container, one process: Caddy serves the files and runs PHP in it, and answers Brotli, zstd and gzip | You want one small process per application instead of a web server plus a PHP pool |
Set the server under the application’s entry in hosting.yaml (schema 1.22 or later), in the
panel’s advanced resource fields, or through the API. The values are fpm_nginx, apache,
and frankenphp.
New Generic PHP applications created from YAML or a repository document default to
php-fpm behind nginx. nginx serves static files directly and passes PHP requests to PHP-FPM.
An explicit webServer: apache selects Apache. Omission on an existing application keeps its
current selection, and explicit webServer: null returns to the recipe default (Apache for Generic
PHP). Applications created directly in the panel or API also follow the recipe default when omitted.
Every shape runs inside your environment's shared Pod, on a listener the platform assigns. A managed WordPress or Moodle site is the exception: it is served by the Pod's shared Apache and PHP, so it runs on Apache only, and the platform refuses another shape for it by field rather than silently building something you did not ask for.
.htaccess is not read, and a build that ships one is refused
Hosting generates the server configuration from your document. Generic PHP's Apache configuration
sets AllowOverride None; nginx does not read .htaccess at all. A .htaccess file therefore
cannot change how requests are handled, so a build whose bundle carries one in the served directory,
below it, or in a directory above it is refused rather than served without the rules you expected.
The failed build names the file it found on the application's Deploy tab, in
hostingctl application build-log and in hostingctl application deployment --json. Remove the file
from what you ship (or move the files it protected outside documentRoot), declare the behaviour
instead, and build again. Every other reason a finished build can be refused is listed in
The build finished, then was refused:
version: "1.19"
applications:
  site:
    runtime: php
    runtimeVersion: "8.5"
    source:
      root: .
    build:
      install: [composer, install, --no-interaction, --no-dev]
    documentRoot: public
    routing:
      mode: front-controller
      entry: index.php
      notFound: 404.php
documentRootis relative tosource.rootand must stay inside the directory you shipped. A root or path that could leave it is refused when the document is read, not when the site fails to start.routing.modeisdirect(only files that exist are served) orfront-controller(an unmatched path reaches your entry script, which is how most frameworks route).routing.indexis the directory index (index.phpwhen you declare none),routing.entryis the front controller's script, androuting.notFoundis served as a real 404 page.
For a Generic PHP migration, run hostingctl application migrate-htaccess ./public/.htaccess
from your project directory. Point it at the file in the intended document root. The command reads
up to 64 KiB locally, with no sign-in. It suggests a routing block for the standard rewrite to a
local PHP script and reports line numbers for directives that need manual review. Check the
suggestion and account for any access restrictions before removing the original file.
HTTP requests for dotfiles and files inside dot directories are refused in both shapes. This does not make an archive a safe place for secrets: keep them out of the bundle.
Composer
The install is yours and the process is the platform's. Declare it, and commit the lockfile:
- A project with a
composer.jsondeclarescomposer install(with--no-interaction --prefer-distif you want them) and itscomposer.lockis what the build carries. - A third build stage restates your install with
--no-dev, so development dependencies are not in the release that serves the site. - A project with no Composer file declares no install at all. The build emits no container for that stage rather than running an empty command, and the tree is packaged as it is.
The build stages run a PHP command-line image of the same minor as the serving image, so a dependency resolved by one minor is parsed by the same one.
Versions, secrets and storage
The version line is chosen per application from the lines your environment offers — see Choose an application's runtime version. A release is always served by the line that built it.
Values in env are delivered to the interpreter, and a {secret: key} reference names a secret this
document declares rather than carrying its value. Keep DATABASE_URL, API keys and tokens in env
references, never in the archive or a committed .env.
Storage volumes are declared like any other application's (storage:, with a volume and a
mountPath). Keep persistent application data on those volumes. PHP code runs as the unprivileged
application identity, the bundle is read-only, and the platform provides the server's temporary
writable paths separately.
Choose an application's runtime version
Most application types let each application choose the language version line it runs on:
| Application type | Lines offered today |
|---|---|
| WordPress | 8.3 (default), 8.4, 8.5 |
| Laravel | 8.3, 8.4, 8.5 (default) |
| Moodle | 8.3 — the line its recipe is qualified for |
| Generic PHP | 8.3, 8.4, 8.5 (default) |
| Node | 24, 26 (default) |
| Ruby | 3.3 (default), 3.4 |
| Go | 1.26, 1.27 (default) |
| Rust | 1.98, 1.99 (default) |
| .NET | 10.0 |
| Python | 3.12, 3.13, 3.14, 3.15 (default) |
| Static HTML | none — a static site has no language line |
The choice belongs to that application alone — another site in the same environment keeps its own line. The platform owns the patch level inside a line, so a security patch arrives as a new image rather than as a choice you have to make. Not every line the platform has published is selectable: an operator can close a line to new work, retire it, or hold it at experimental.
The panel shows the lines your application type offers and, beside any line that cannot be chosen today, the reason. We do not offer a line whose images are not published, because the platform would have nothing to run.
Asking for an upgrade
An upgrade is requested first and run afterwards, and the panel keeps the two apart:
- requested is what you asked for. It is saved immediately.
- running is what your site is actually served by. It changes only when the new PHP has started and answered its health check inside your environment.
Your site restarts while this happens, and how much that interrupts depends on how it runs. A site sharing one runtime with others keeps answering on the old version until the new one is proven. A site in its own runtime keeps answering while a new release is built, but the restart that replaces it can briefly take it out of service — a failed start leaves the old runtime and the old version in place. We do not promise zero downtime for that restart.
Until the change completes, the version your site runs is still the old one, and that is what the panel reports; the version you asked for is shown separately.
A move down onto a line that is still open to new work is accepted, so you can undo your own change — that is a new forward release, never a restored artifact. A move onto a line that has been closed to new work (deprecated, closing, or being evacuated) is refused, and a line whose rows block re-entry refuses it too. A line an operator granted your company access to is the exception: the grant is what lets a closed line take one more move.
We do not check your plugins, themes or application code against the new version. The health check proves the platform's own runtime started, not that your code is compatible. Test the site on the new version before you rely on it, and expect a plugin that targets an older PHP to complain after the move rather than during it.
From a terminal, hostingctl environment runtime-versions --company <slug> lists every type's lines, which
of them may be chosen now and why not, and hostingctl application runtime-version <environment-uuid> <application-uuid> --company <slug> --version <line> moves one application onto another line. The same
choice is accepted when you create an application.
Get a specific deployed version
Every release is built from a recorded commit, and the application's Deploy tab names it beside the release. To run or inspect a version that was deployed before, check out that commit in your repository: that is the exact source the release was built from. Releases are immutable — the running one is never edited in place, and a rollback re-serves a bundle that was built earlier rather than rebuilding anything.
The release that is serving also offers Download this release, which downloads its built bundle. That is what the platform runs, not your source: to change it you change the repository and deploy again. Older releases are not downloadable — the link exists only for the one that is serving, so a saved link stops working when a newer release replaces it.
When a push deploys
Deploying from a repository is a choice, not a default:
- with Deploy automatically when this branch changes on, a push to that branch builds and deploys by itself;
- with it off, a push changes nothing until you select Build and deploy on the application's Deploy tab.
Either way, whoever can write to that branch can run code beside your application's runtime secrets, so the switch is an access decision as much as a convenience.
Seeing whether your pushes are arriving
The application's page opens on one status line (live, deploying, or needs attention and why), and its Deploy tab answers two different questions, deliberately separately:
- Did GitHub talk to us? The repository panel shows the last delivery it sent — its event, when it arrived, and
whether the platform has handled it.
Arrived and not handled yetis normal for a few seconds. If a delivery is still unhandled after ten minutes the panel says so, and says who retries: the platform re-sends a delivery it never handled, so a stuck one is answered by pushing the commit again rather than by resyncing the repository — resyncing only re-reads the branch. Each delivery the platform handles is also marked handled, so an application that built nothing is never mistaken for one where nothing arrived. - What did the platform decide? When a push arrives for your branch and builds nothing, the Deploy tab says which push it was, why, and what that means for you: a push naming the commit you already serve needs nothing from you, a push the repository places behind the release you serve was already passed, and a push whose commit could not be compared with the served one is answered by selecting Build and deploy on the Deploy tab. A push that deployed itself says nothing extra — it is the ordinary case.
Neither message claims a build or a deployment succeeded. A delivery being acknowledged means GitHub's event reached us; the build and release states in the same panel are the authoritative answer about what is running.
Next
- Give an application an address you own: Web addresses.
- See how an application is described, and what it can reference: Configuration.
- Read or change its database: Databases.
- Tail its output: Logs.